Identify Risks And Opportunities
Although risks and opportunities have to be determined and addressed, there is no requirement for a formal, documented risk management process in ISO 9001. However, you should ensure that your organization has a methodology that enables it to effectively identify and evaluate risks and opportunities when planning its quality management system.
Contents
- Should You Document Your Risks & Opportunities Procedure?
- How Do You Address Risk and Opportunities?
- Why Is Risk Management Important?
- What About Outsourced Processes?
- How To Develop Your Risk Management Process
- How To Develop Your Risk Management Methodology
- What Risk Management Documents Do I Need?
- Who Is Responsible For Risk Management?
- Should I Use A Risk Register?
- How Do I Report Risk Management Data?
- How Do I Audit A Risk Management Processes?
- What Is The Risk Evaluation Process?
- Taking A Planned Approach To Address Risks
- How Do I Evaluate Opportunities?
- How Should I Communicate Risks And Opportunities?
- Risk & Opportunities Template

- Risk Management Toolkit

Should You Document Your Risks & Opportunities Procedure?
We recommend yes.
Although risks and opportunities have to be determined and addressed, there is no requirement for a formal, documented risk management process. However, the risk and opportunity register will provide your organization with a consistent methodology to capture, assess, and prioritize strategic and operational risks and opportunities concerning your management system and its objectives.
- Conduct risk identification workshops to gather stakeholders to discover risks and opportunities using tools like brainstorming
- Document the risks and opportunities by populating structured rows in the register with detailed risk descriptions
- Assess the likelihood and consequence using qualitative or quantitative methods
- Assign risk owners to ensure that every risk and opportunity has a designated accountable party
- Develop risk mitigation plans to either accept, avoid, transfer, or share the risk
- Establish regular reviews by setting weekly, monthly, or milestone-based evaluations
The procedure aims to outline your organization’s risk and opportunity management framework and activities.
If you are looking for information regarding ISO 45001, please see our Hazard Identification & Risk Assessment Procedure webpage.
Don’t Try to Manage It All Alone!

Reference to risk-based thinking is present in the following clauses of the standards:
- Determine and address risks (Clause 4.4.1)
- Promote risk-based thinking (Clause 5.1.1)
- Ensure risks determined and addressed (Clause 5.1.2)
- Determine risks that need to be addressed to achieve intended results (Clause 6.1.1)
- Plan actions to address risks; integrate into processes; evaluate effectiveness of actions (Clause 6.1.2)
- Control those risks identified (Clause 8.1)
- Evaluate effectiveness of actions on risks (Clause 9.1.3)
- Review effectiveness of actions on risks (Clause 9.3.2)
- Improve the QMS responding to risk (Clause 10.1)
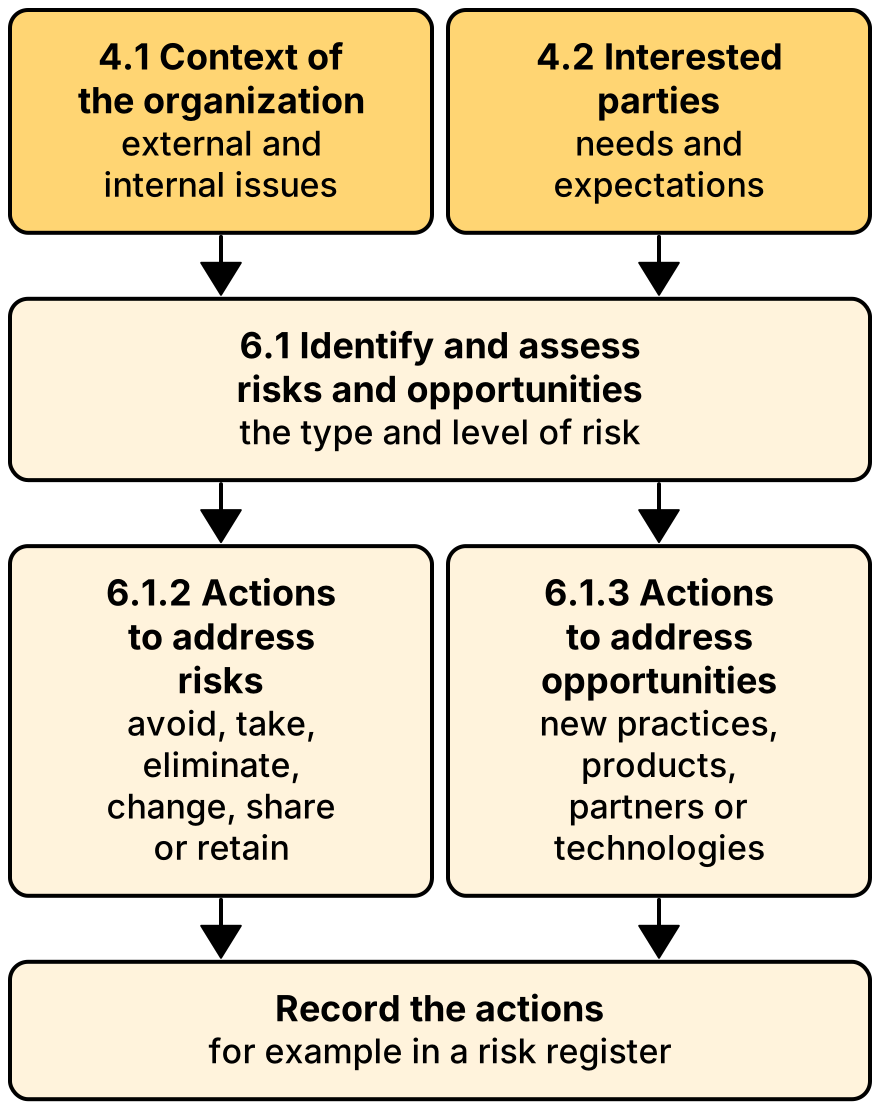
The risks and opportunities should be relevant to the context of your organization (Clause 4.1), as well as any interested parties (Clause 4.2). You should ensure that your organization has applied this risk identification methodology consistently and effectively.
How Do You Address Risk and Opportunities?
In the absence of documented processes/procedures, you may need to use observations and interviews (and a review of the process output, which may contain documented evidence) to assess the processes that determine whether or not undocumented processes are being carried out as planned.
External and internal issues and the relevant needs and expectations of relevant interested parties may be sources of risks and opportunities.
Each quality management system’s processes do not represent the same level of risk regarding your organization’s ability to meet its objectives. Due to this reason, the consequences of failures or non-conformities in relation to processes, systems, products, and/or services will not be the same for all organizations.
Start with Expert Templates, then Make Them Yours

When deciding how to plan and control the QMS, including its component processes and activities, your organization needs to consider both the type and level of risk associated with them.
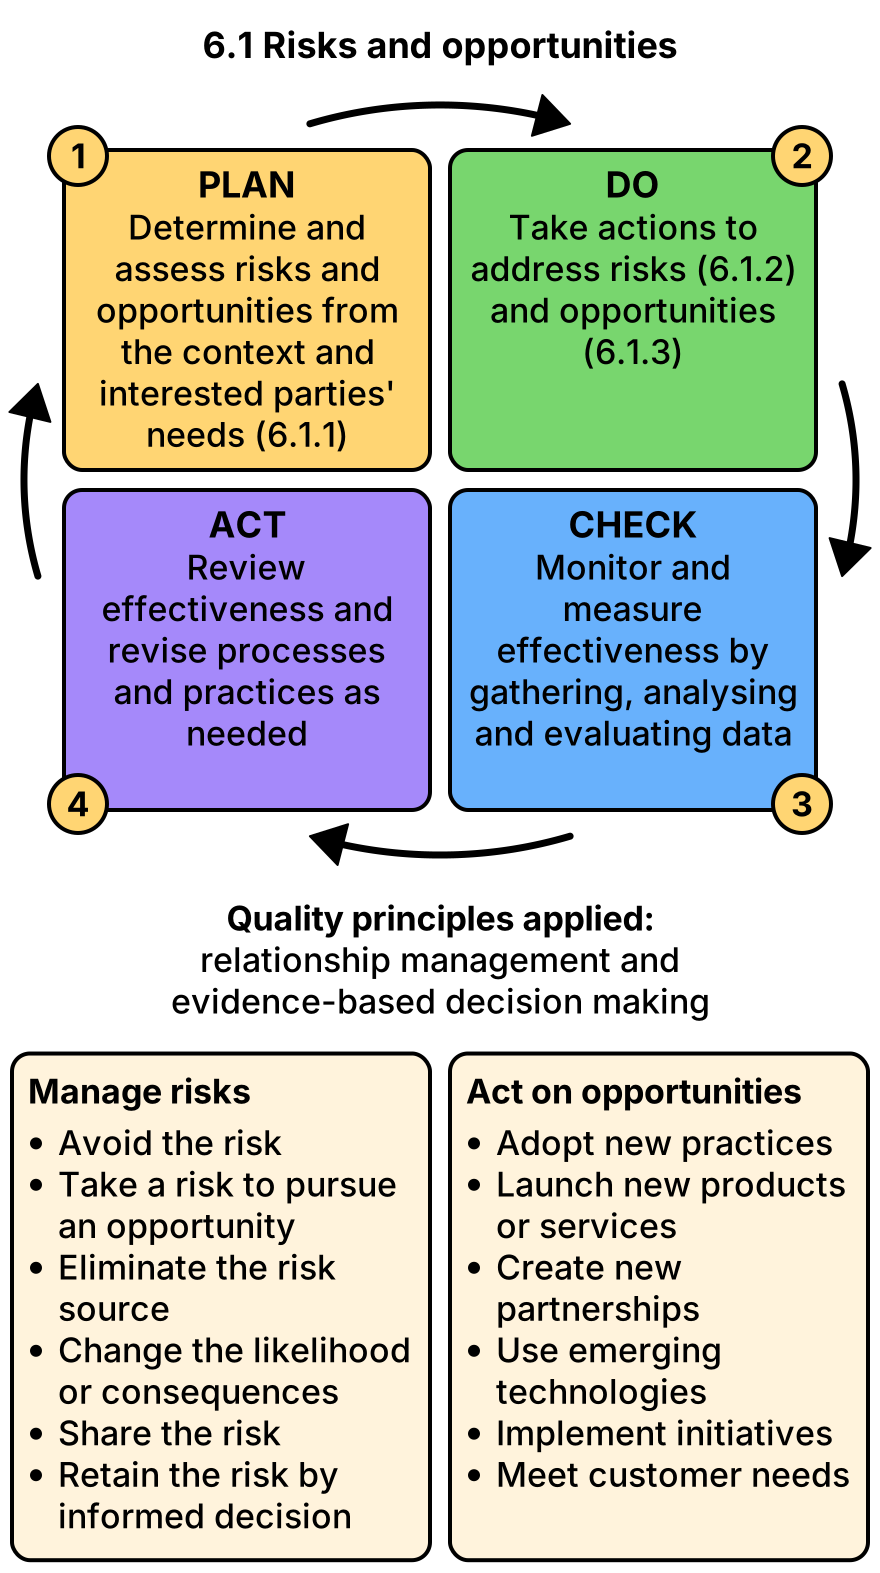
Ensure that your organization takes a planned approach to addressing risks and opportunities, and that any actions taken have been recorded. Options to address risks and opportunities can include:
- Avoiding risk
- Taking risks to pursue an opportunity
- Eliminating the risk source
- Changing the likelihood or consequences
- Sharing the risk
- Retaining risk by informed decision
- SWOT analysis by the organization as part of its business strategy to identify the external risks and opportunities, and an action plan to address them
- Formal business risk assessment performed by the organization, taking into consideration its context, associated risk, and opportunities, and mitigation plan
- Use of the process approach by the organization to identify sources of input, activities, output, receiver of output, performance indicators to control and monitor processes, the risks and opportunities associated with them, and an action plan to address them
Why Is Risk Management Important?
The concept of risk in the context of ISO 9001 relates to the uncertainty in achieving the objectives of the QMS. Risk management is essential, since risk and opportunities will underlie every aspect of your organization’s operations. Understanding the risks and opportunities your business faces, and managing them appropriately, will enhance your business’s ability to make better decisions and achieve your objectives.
Businesses should view the management of risks to their people, assets, and all aspects of their operations as an essential responsibility. Implement and maintain a risk management process to protect and support your organization’s responsibilities. A practical risk and opportunity management approach is not only good business practice but also provides organizational resilience, confidence, and benefits, including:
- Provides a rigorous decision-making and planning process
- Provides the flexibility to respond to unexpected threats
- Takes advantage of opportunities and provides a competitive advantage
- Equips managers with tools to anticipate changes and threats, and to allocate appropriate resources
- Assures Top Management and stakeholders that critical risks are being managed
- Enables better business resilience and compliance management
What About Outsourced Processes?
Your organization might outsource the provision of some processes or the manufacture of components, subassemblies, or entire units. To maintain control over the processes, your organization should incorporate appropriate risk management activities for these processes and products by planning and ensuring risk control measures are appropriately applied.
If risk control measures are applied to outsourced processes or products, the risk control measures and their importance should be documented within the purchasing data or information and clearly communicated to the supplier.
Before the approval and implementation of a change to any outsourced process or product, your organization should:
- Review the change
- Assess if new risks have been discovered; and,
- Determine if the current and/or new individual residual risks and/or the overall risk is acceptable according to the predetermined existing acceptability criteria
If risk control measures are applied to outsourced processes or products, the risk control measures and their importance should be documented within the purchasing data or information and clearly communicated to the supplier.
Clauses That Promote Risk-based Thinking
Risk-based thinking is probably already part of your organization’s process approach, as it forms a key part of preventive action routines. Risk is often thought of in the negative sense but risk-based thinking can also help identify opportunities and advantages, which is the positive aspect of risk management.
There are six clauses in ISO 9001 that require your organization to consider risks and opportunities:
- Clause 4.4.1 requires your organization to determine the risks which can affect its ability to meet the system objectives. Risk-based thinking means considering risk quantitatively as well as qualitatively, depending on the business context.
- Clauses 5.1.1 and 5.1.2 require Top Management to demonstrate leadership and commit to ensuring that risks and opportunities that can affect the conformity of a product or service are determined and addressed.
- Clauses 6.1.1, 6.1.2 and 6.1.3 each require your organization take action to identify risks and opportunities, and plan how to address the identified risks and opportunities.
- Clause 8 requires your organization to plan, implement and control its processes to address the actions identified in Clause 6.
- Clause 9 requires your organization to monitor, measure, analyze and evaluate the risks and opportunities.
- Clause 10 requires your organization to improve by responding to changes in risk.
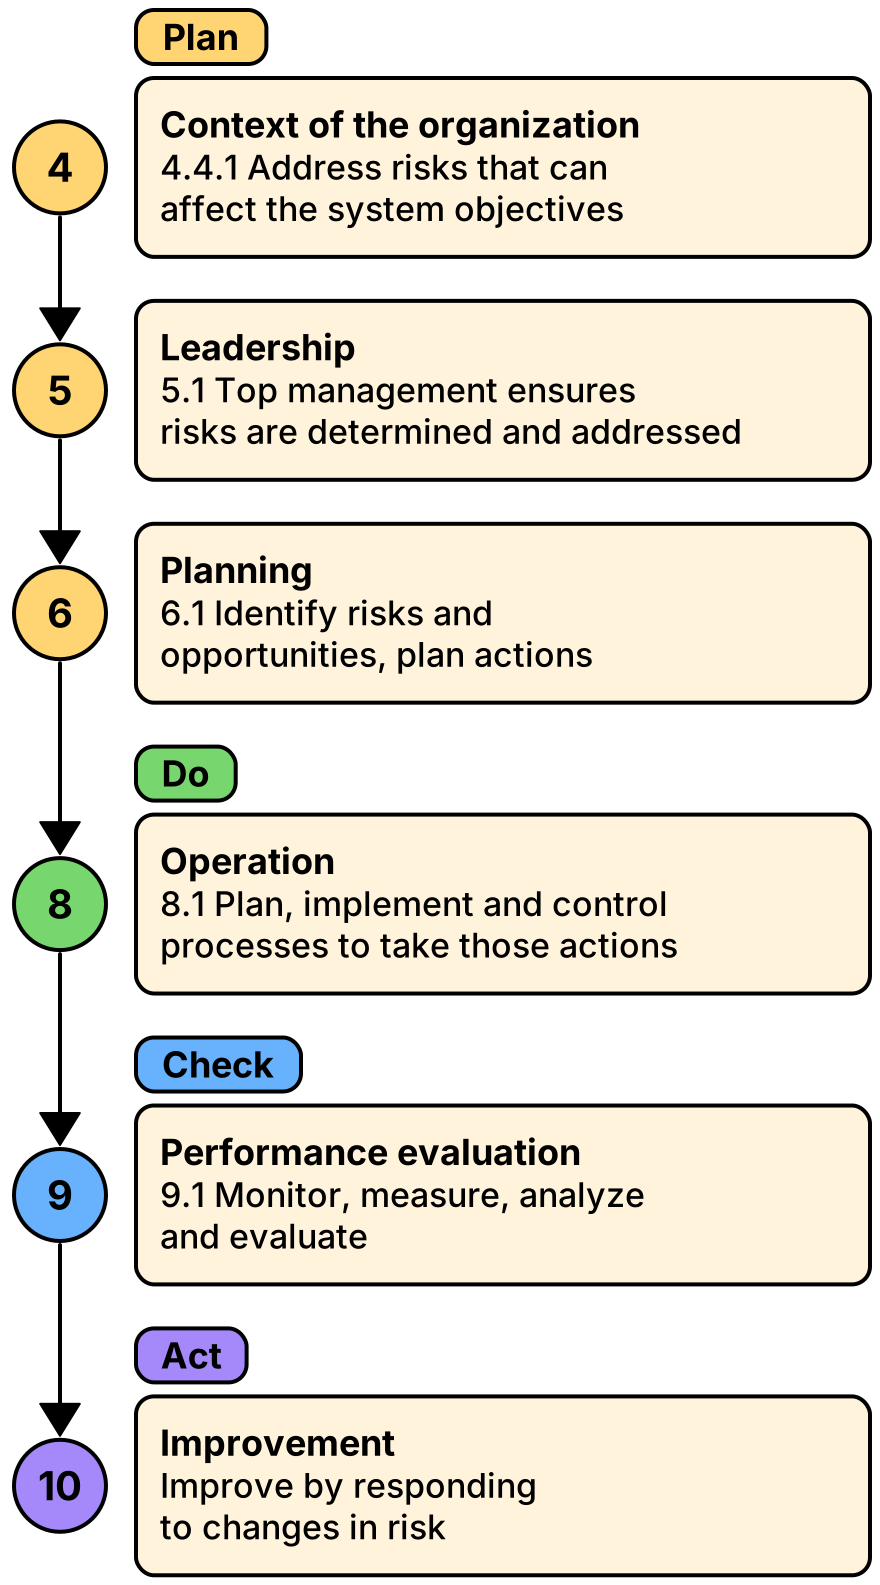
The adoption of risk-based thinking will, over time, improve customer confidence and satisfaction by assuring the consistency of the quality of goods and services brought on by establishing a culture of prevention and improvement.
Jump Start Your Documentation


How To Develop Your Risk Management Process
Understanding risks and opportunities and managing them appropriately will enhance your organization’s ability to make better decisions, safeguard assets, enhance your ability to provide products and services, and achieve your mission and goals.
By developing a risk management process and considering risks and opportunities throughout your organization, the likelihood of achieving its stated objectives is much improved as the output becomes more consistent, and customers can be confident that they will receive the expected product or service.
Risk-based thinking, therefore, helps to:
- Improve stakeholder confidence and satisfaction
- Assure the consistency of quality of goods and services
- Establishes a proactive culture of prevention and improvement
- Intuitively take a risk-based approach
We suggest that you use the familiar Plan-Do-Check-Act (PDCA) methodology to manage your organization’s transition to risk-based thinking, using an approach that ring-fences processes into risk groups such as:
- Business planning and strategic direction
- Process risk and opportunity
- Product and service risk and opportunity
- Risk and opportunities associated with the control of externally provided products and services
| Risk Group | PDCA | Clause References | Activity |
|---|---|---|---|
| Business planning and strategic direction | Plan | 4.1, 4.2 | Has the organization identified internal and external issues and interested parties that are relevant to and/or support the organization's strategic direction? |
| Do | 5.2.1 | Is the strategic direction being utilized as an input to the quality policy, objectives, risk and opportunity management, and the management review processes? | |
| Check | 4.1, 4.2, 5.1.1, 9.3.2 | Is the QMS being assessed and reviewed in accordance with the strategic direction? | |
| Act | 10.3 | Is the QMS being updated as necessary in response to any of the above changes? | |
| Process risks and opportunities | Plan | 4.4.1, 6.1, 6.2, 6.3, 8.5.6 | Have risks and opportunities to achieving process objectives been identified when establishing the QMS and planning for change? |
| Do | 8.1 | Have the identified process risks and opportunities been addressed? | |
| Check | 6.1.2, 9.1.3, 9.3.2 | Is the organization analyzing the effectiveness of actions taken to address process risks and opportunities? | |
| Act | 10.2.1, 10.3 | Following analysis and corrective action, is there evidence that process risks have been updated? | |
| Product and service risks and opportunities | Plan | 5.1.2, 6.1, 6.2, 8.1, 8.2.2, 8.2.3, 8.3.2 |
Have risks and opportunities to achieving product or service conformity been considered?
|
| Do | 8.1, 8.2.3.1, 8.3.3 | Have design and operational controls to address the identified product and service risks and opportunities been implemented? | |
| Check | 9.1.3, 9.3.2 | Is the organization analyzing the effectiveness of actions taken to address product risks and opportunities? | |
| Act | 10.1 | Has the organization determined and selected opportunities for improvement on the product and service? | |
| Risk and opportunities associated with the control of externally provided products and services | Plan | 6.1 | Have risks associated with externally provided products, processes (i.e., formerly named outsourced), or services been identified? |
| Do | 8.4.1, 8.4.2 |
Are the identified risks utilized as an input into the:
|
|
| Check | 8.4.1, 9.3.2 | Has the organization applied criteria for evaluating, selecting, monitoring performance, and re-evaluating external providers? | |
| Act | 9.3.3 | Has the organization modified the controls applied to external providers based on the results of the evaluation? |
How To Develop Your Risk Management Methodology
Risks and opportunities will influence every aspect of your organization’s operations. Understanding the risks and managing them appropriately will enhance your organization’s ability to make better decisions, safeguard assets, and enhance your ability to provide products and services and to achieve your mission and goals.
By considering risk and opportunity throughout your organization, the likelihood of achieving stated quality objectives is improved, output is more consistent, and customers can be confident that they will receive the expected product or service.
Risk-based thinking, therefore, helps to:
- Improve customer confidence and satisfaction
- Assure consistency of quality of goods and services
- Establishes a proactive culture of prevention and improvement
- Intuitively take a risk-based approach
We suggest that you use the familiar Plan-Do-Check-Act (PDCA) methodology to manage your organization’s transition to risk-based thinking.
What Risk Management Documents Do I Need?
Documented information resulting from risk and opportunity management activities, such as risk management processes, plans, and reports, should be maintained or referenced in either a risk management file or other appropriate sources:
- Design history file
- Technical file/documentation
- Device master record
- Device history record
- Process validation files
Your organization should consider the benefits of integrating the risk and opportunity management processes, documents, and records into your quality management system. The advantage of this could be a single document control system, ease of use and review, accessibility, retention, etc.
Document controls, including document change controls, for risk and opportunity management system documentation should be the same as the controls for quality management system documentation. This documentation can be in any form or type of medium.
Why Reinvent The Wheel?

Who Is Responsible For Risk Management?
Your organization should ensure that it has documented and clarified the roles, responsibilities, accountabilities, and authorities at all levels of the business to address risk and opportunity management.
This ensures that a risk and opportunity management approach is embedded in your operations through a number of communication, training, and support systems.
Risk and opportunity management responsibilities, accountabilities, and authorities should be set out in the following documented information:
- Risk and opportunity management policy
- Job/position descriptions
- Internet/intranet
- Project/process/product/service documentation
- Performance planning and review documentation
The top management team should retain ultimate authority and responsibility for the risk and opportunity management process, and they should ensure that the risk management framework is established, implemented, monitored, and reviewed for improvement.
Accountable managers are responsible for:
- Establishing, using, and maintaining the risk and opportunity management process
- Ensuring that the risk management process is communicated and integrated throughout the organization and that risks are identified, managed, and monitored in accordance with this process
- Ensuring that adequate resources from all necessary disciplines are allocated to support this process
- Ensure that risk treatment strategies are developed and implemented, and controls are maintained
Employees at all levels are responsible for managing risks and opportunities per this process in their respective areas of concern.
Should I Use A Risk Register?
While not mandated by ISO 9001, risk registers can help identify and record the risks and opportunities facing different areas of the business, and identifying risk is a critical step in managing it.
Identifying risks and opportunities is a critical step in managing them, and the risk and opportunity register allows your organization to assess the risks and opportunities in context with its overall strategy and help record the controls and treatments of those risks.
Risk and opportunity identification should be carried out with the full involvement of the relevant parties to ensure the relevant perspectives and expertise are represented (e.g., appropriately qualified representatives from various functions, contractors, stakeholders, suppliers, and specialists as appropriate).
Risk and opportunity registers will allow your organization to assess the risk in context with the overall context of your organization. They will help to record the controls and treatments of those risks. Risk registers can be developed in tiers:
- Strategic level
- Operational level
- Process level
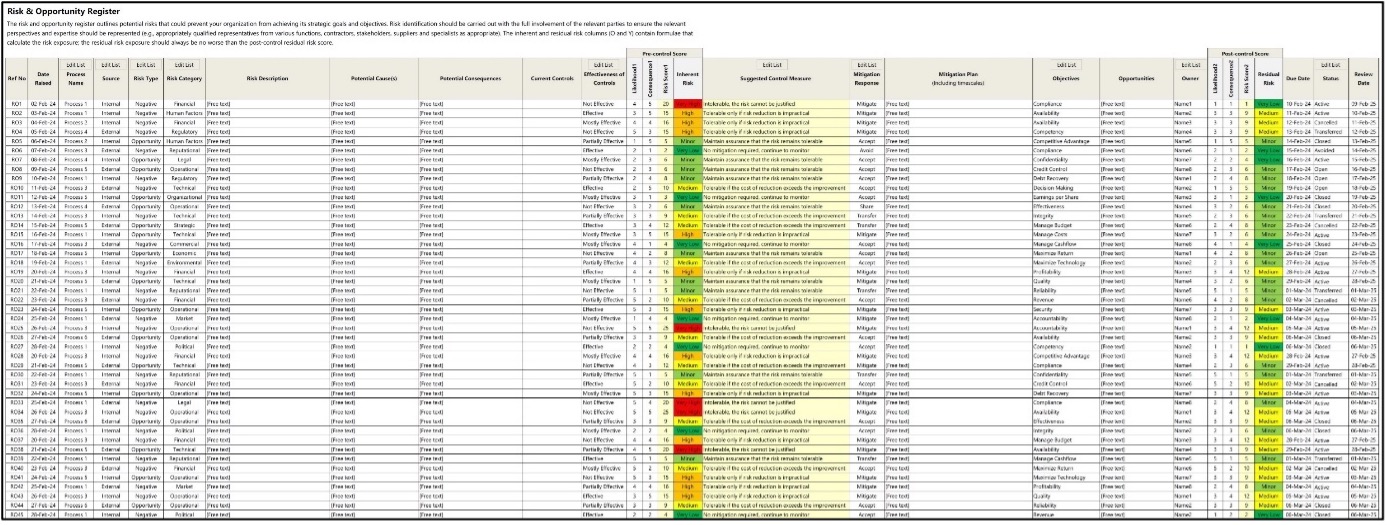
Our risk and opportunity register outlines potential risks that could prevent your organization from achieving its strategic goals and objectives. The inherent and residual risk columns contain formulae that calculate the risk exposure; the residual risk exposure should always be no worse than the post-control residual risk score.
The risk and opportunity register workbook contains multiple worksheets and has been formatted in a table layout, with each cell containing either predefined text, drop-down menus, formulae, or conditional formatting.
The risk and opportunity register offers the technical functionality needed for effective risk management by providing a structural foundation with a comprehensive 8-worksheet framework, based on the ISO-31000-1-2018 Risk Management – Guidelines.
The risk management framework includes guidance, automated scoring, pivot table reporting, and interactive charts:
- Guidance and quick start guide
- Risk and opportunity register
- Risk rating matrix
- Summary charts
- Process report
- Status report
- Risk report
- Issue report
The risk and opportunity registers or risk logs become essential as they record the identified risks, their severity, and the action steps to be taken. It can be a simple document, spreadsheet, or database system, but the most effective format is a table.
The risk and opportunity register consists of the following columns, shown in the table below. The ‘Ref’ column in the table below is the identifier for a particular column in the risk and opportunity register:
| Ref | Item/Title | Data Type | Purpose |
|---|---|---|---|
| A | Ref No | Predefined text | Unique risk ID number. |
| B | Date Raised | Autoformat date | Enter the date the risk or opportunity was discovered, or when it was recorded in the register. |
| C | Process Name | Drop-down | In which process, department, or activity is the risk or opportunity present? Edit the process name list to match your organization. |
| D | Source | Drop-down | Include all risks, whether or not their source is under the organization's control. |
| E | Risk Type | Drop-down | A risk is the effect of uncertainty. If the risk is a threat, select 'negative'. If the risk is positive, select 'opportunity' from the drop-down menu. |
| F | Risk Category | Drop-down | Risk categories are classifications used to group potential sources of risk, allowing organizations to better understand, manage, and mitigate threats. Edit the category list to match your terms. |
| G | Risk Description | Free text | The risk description should be a clear, concise statement that defines the specific issue and what could go wrong. |
| H | Potential Cause | Free text | Is the root-cause identifiable? If so, briefly describe. |
| I | Potential Consequences | Free text | What may be a result of this risk? Describe the potential consequences, either positive or negative, of the risk. |
| J | Current Controls | Free text | Are there controls or measures that maintain or modify the risk? Describe what process, policy, device, practice, or other actions currently modify risk. If there are no controls in place, type 'none'. |
| K | Effectiveness of Controls | Drop-down | Select the option that describes the effectiveness of existing controls to avert the risk. Edit the effectiveness list to match your terms. |
| L | Likelihood1 | Drop-down | What is the chance of the risk occurring? 1 = Very low, 2 = Minor, 3 = Medium, 4 = High, or 5 = Very High. |
| M | Consequence1 | Drop-down | What is the effect of the foreseeable consequences? 1 = Very Low, 2 = Minor, 3 = Medium, 4 = High, or 5 = Very High. |
| N | Risk Score1 | Formula | The risk score is calculated as L x C. Ensure cell formulae are not overwritten. |
| O | Inherent Risk | Formula and conditional formatting | Inherent risk is the level of risk that exists before any new controls or mitigation measures are applied. |
| P | Suggested Control Measure | Formula and predefined text | Based on the inherent risk rating, these cells will propose a suggested control measure per the risk rating matrix. Edit the risk treatment list to match your terms/definitions. |
| Q | Mitigation Response | Drop-down | Input the type of control measure you intend to implement to deal with the negative consequences. Edit the mitigation list to match your terms. |
| R | Mitigation Plan | Free text | Specify how the chosen mitigation option will be implemented. |
| S | Objectives | Drop-down | Briefly state the goals and objectives by which the control measures can be monitored. Edit the objectives list to match your terms/definitions. |
| T | Opportunities | Free text | Opportunities are circumstances that are favourable to objectives, in which gain is likely. Describe any positive effects that arise from the risk. |
| U | Owner | Drop-down | A person or entity with the accountability and authority to manage the risk by implementing and monitoring the control measures. Edit the owner's name. |
| V | Likelihood2 | Drop-down | What is the chance of the risk occurring? 1 = Very low, 2 = Minor, 3 = Medium, 4 = High, or 5 = Very High. |
| W | Consequence2 | Drop-down | What is the effect of the foreseeable consequences? 1 = Very Low, 2 = Minor, 3 = Medium, 4 = High, or5 = Very High. |
| X | Risk Score2 | Formula | The risk score is calculated as L x C. Ensure cell formulae are not overwritten. |
| Y | Residual Risk | Formula and conditional formatting | Residual risk is the remaining risk after risk treatment. The residual risk score must be lower after implementing the control measures. |
| Z | Due Date | Autoformat date | Enter the date when the control measures were implemented. |
| AA | Status | Drop-down | What is the current status of the risk? Has the risk been successfully mitigated or not? 1. Open, 2. Active, 3. Closed, 4. Cancelled, 5. Avoided, or 6. Transferred. |
| AB | Review Date | Autoformat date | Enter the date when the control measures are to be reviewed. |
The risk and opportunity register must be maintained continuously and updated to reflect new issues as and when they emerge. Formally review the risk and opportunity register within management review meetings and document the results of the review within the minutes of the meetings.

How Do I Report Risk Management Data?
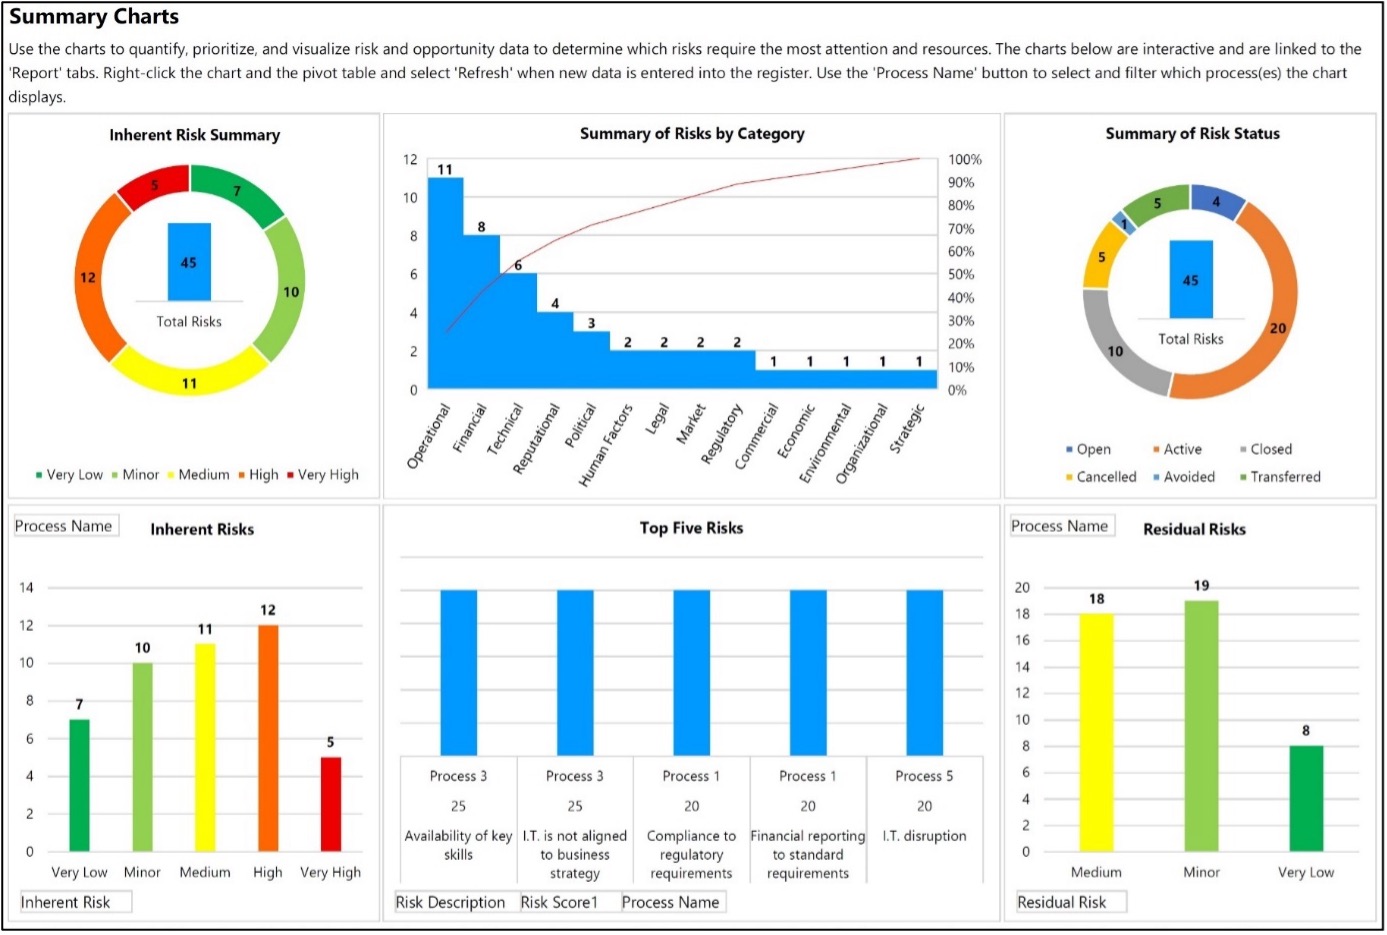
The summary charts dashboard with the risk and opportunity register provides data-driven insights to help you visualize and report risk management data, track progress, and communicate issues to stakeholders.
The charts facilitate quantitative comparisons between various processes and their risks, and the risk and opportunity register workbook generates data-driven recommendations and prioritizes the most frequent or serious problems.
Use the charts to provide visual representations of the data for executive-level reporting and strategic decision-making to help prioritize data to determine which risks and opportunities require the most attention and resources.
The following charts are interactive, and you can use the drop-down menus on the chart to select and filter which processes or risks the charts display.
- Inherent Risk Summary
- Summary of Risks by Category
- Summary of Risk Status
- Inherent Risks
- Top Five Risks
- Residual Risks
- Inherent Risk v Residual Risk Exposure
- Risks by Process
- Types of Issues by Process
- Risks and Opportunities by Process
- Summary of Pre & Post-control Risks
The risk and opportunity register also contains four specialized report sheets, each with interactive pivot tables that summarize and analyze the risk and opportunity entries from the main risk register worksheet. Interactive features across all reports include filtering and sorting capabilities.
- Process report
- Status report
- Risk report
- Issue report
These reports collectively provide a comprehensive risk management dashboard that supports different stakeholder needs, from operational process owners to executive management, enabling informed decision-making about risk priorities, resource allocation, and control effectiveness.
How Do I Audit A Risk Management Processes?
The primary objective of auditing the risk management process is to provide an assurance framework that underpins the risk management process.
This should include reviews of processes and controls over high risks as determined through the risk planning process.
The internal audit function provides an independent appraisal of the adequacy and effectiveness of internal controls. Recommendations should be provided, where applicable, for improvements to controls, efficiency, and effectiveness of processes.
| Ref. | Risk & Opportunity Requirements | Yes/No | Evidence /Documents |
|---|---|---|---|
| 9.1.1 |
When planning for the quality management system, has your organization considered the issues referred to in 4.1, the requirements referred to in 4.2, and determined the risks and opportunities that need to be addressed to give assurance that the quality management system can achieve its intended results?
|
||
|
Has your organization considered the issues referred to in 4.1 and the requirements referred to in 4.2 and determined the risks and opportunities that need to be addressed to enhance desirable effects? |
|||
|
Has your organization considered the issues referred to in 4.1 and the requirements referred to in 4.2 and determined the risks and opportunities that need to be addressed to prevent, or reduce, undesired effects? |
|||
|
Has your organization considered the issues referred to in 4.1 and the requirements referred to in 4.2 and determined the risks and opportunities that need to be addressed to achieve improvement? |
|||
|
When planning for the quality management system, has your organization considered the issues referred to in 4.1, the requirements referred to in 4.2, and determined the risks and opportunities that need to be addressed to give assurance that the quality management system can achieve its intended results? |
|||
| 9.1.1 | Does your organization plan actions to address risks and opportunities? | ||
| Does your organization plan actions to integrate and implement the actions into quality management system processes? | |||
| Does your organization plan actions to evaluate the effectiveness of any actions? | |||
| Does your organization ensure that the action taken to address risks and opportunities is proportionate to the potential impacts on the conformity of products and services? |
What Is The Risk Evaluation Process?
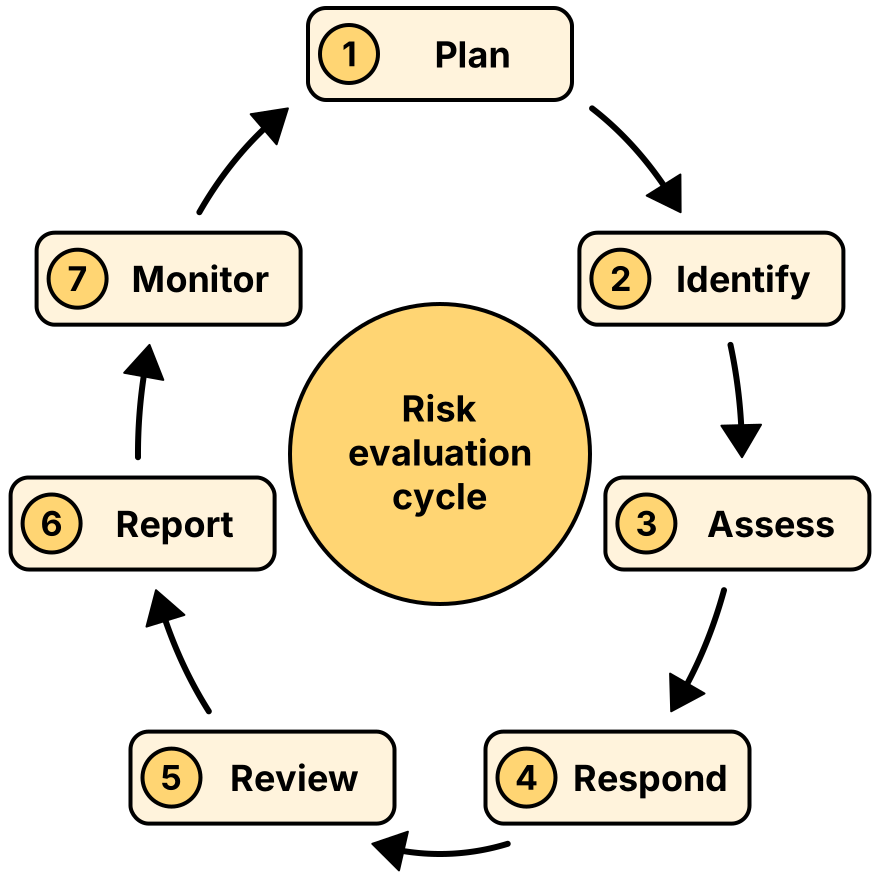
Risk evaluation should become embedded in your organization’s day-to-day operations. It should be undertaken at all levels throughout your business to ensure that capabilities and resources are employed efficiently and effectively to manage opportunities and threats. The risk evaluation process is represented as a seven-step, cyclical process:
Step 1: Plan
Your organization should develop and document a plan that briefly describes how and when risk, in the form of strengths, weaknesses, opportunities, and threats, will be assessed and who will be involved. This should reflect the scope (including its complexity, interfaces, etc.), policies, and objectives. Risks have three components:
- A future root cause (yet to happen), which, if eliminated or corrected, would prevent a potential consequence from occurring;
- A probability (or likelihood) assessed at the present time of that future root cause occurring;
- The consequence (or effect) of that future occurrence.
Risks should not be confused with issues. If a root cause is described in the past tense, the root cause has already occurred, and hence, it is an issue that needs to be resolved, but it is not a risk.
Step 2: Identify
In this step, your organization should systematically identify those risks associated with the scope of the process that could significantly affect the achievement of objectives and product conformity. The aim is to generate a comprehensive list of sources of possible risks and future events that could impact the objectives of delivering quality products to your customers on schedule and on budget.
While several categories of risk are associated with manufacturing, including strategic, financial, and operational, customers and suppliers are generally concerned with the operational risks associated with the quality and schedule performance requirements of the products they purchase.
Risk identification should be carried out with the full involvement of the relevant parties to ensure the relevant perspectives and expertise are represented (e.g., appropriately qualified representatives from various functions, contractors, stakeholders, suppliers, and specialists as appropriate.
Risk identification involves the relationship between your organization and the broader external environment or community. A range of issues should be considered in examining the strategic content, including:
- Opportunities and threats associated with the local, regional, state, and global economic, social, political, cultural, environmental, regulatory, and competitive environments;
- Key thrusts of stakeholder strategies;
- Strengths and weaknesses of attaining objectives.
The internal context process is intended to provide a plan for managing the significant risks to achieving quality, schedule, and cost requirements associated with the manufacture and delivery of products in accordance with customer and/or regulatory requirements. This process supports your company’s policy and assists in achieving established objectives.
Operational risk identification involves gaining an understanding of the organization’s capabilities, goals, objectives, strengths, and weaknesses by considering the following:
- Organizational structure and culture;
- Geographical/demographical;
- The identity and nature of interaction with key internal or external stakeholders;
- The existence of any operational constraints;
- Objectives and key performance indicators;
- Business resilience vulnerabilities;
- Relevant issues relating to recent change management risk, performance, or audit reviews;
- Relevant stakeholder community concerns or requirements;
- Regulatory and contractual requirements and constraints;
- Management system requirements.
Having identified all associated risks that could impact your business or its management system, the process of rating the risks for significance can be carried out. This crucial process, together with a thorough knowledge of legal and other similar requirements, provides the foundations of the management system.
Step 3: Assess
The risk evaluation rating is based on a 5 x 5 matrix with five levels of risk (i.e., very low, low, medium, high, and very high). The matrix presents examples of risk likelihood rankings and risk consequence rankings for issues relating to health and safety, environment, quality, delivery, cost, and programme.
Each risk should be evaluated and scored, using the risk register, in accordance with the defined risk parameters identified below. The goal is to identify the 'high' and 'very high' priority risks and focus risk mitigation resources on them as the risk management programme evolves over time.
This assessment process is vital in determining the need for controls aimed at either reducing risk to levels deemed to be tolerable or meeting the requirements of the legislation. The significance level (or risk rating) should then be used to prioritize actions. Remember that the importance of this process cannot be overestimated. If you get this process wrong, the whole system will be suspect.
Assessing the severity of risk should drive management attention and support the planning for risk mitigation. Quantitative risk assessments can be undertaken to provide an improved understanding of the risk profile and derive a more detailed understanding of specific cost and time risks. The output also supports decision-making and the monitoring of risk management activities.
The likelihood element is determined using the criteria specified in the following criteria, and a score of 1 to 5 is assigned. The level is determined by evaluating all available current and historical information or by estimating the probability of occurrence using experience and judgment as a guide.
| Score | Likelihood | Percentage | Probability | Judgment |
| 0 | Unrated | N/a | N/a | N/a |
| 1 | Very Low | <0.1% | 1 in 1,000 | Not likely |
| 2 | Minor | 1% | 1 in 100 | Low likelihood |
| 3 | Medium | 1-49% | 1 in 2 | Quite likely |
| 4 | High | 50-94% | 0.75 in 1 | Highly likely than not |
| 5 | Very High | >95% | 1 in 1 | Almost certain |
The consequence element is determined using the criteria specified in the following criteria, and a score number with the risk register is assigned. The consequence is an undesirable event or impact that would negatively affect the management system should the risk materialize. Consequence is a subjective ranking made using experience, historical data, or comparison to other systems.
| Score | Impact | Health & Safety | Environment | Quality |
| 0 | Unrated | N/a | N/a | N/a |
| 1 | Very Low | Non-reportable accident or injury | No measurable environmental impact or harm. No corrective action is required. | Non-compliance with standards or procedures that can be managed. Requires minor rework to bring into full conformity |
| 2 | Minor | Reportable minor injury. Multiple non-reportable minor injuries | Environmental impact is confined to the site. No significant harm, but corrective action is required | Developed components or systems may not receive approval through the assurance process. Requires significant rework to bring into full conformity |
| 3 | Medium | Major injury/illness. Multiple reportable minor injuries | 3rd Party impact. Short-term environmental impact, but no significant harm | Failure to manufacture or construct an approved component or system to meet design or specification. Extensive rework or remake. Requires customer concession |
| 4 | High | Single Fatalities. Multiple major injuries | Significant harm to the environment that is repairable. Breach of legislation | Failure of a major component or system leads to rejection. Multiple scrapped parts. Multiple parts require repair to restore them to an acceptable condition |
| 5 | Very High | Single or multiple fatalities | Significant harm to the environment that is permanent or has long-term effects | Catastrophic failure of a major component or system to function in temporary or permanent conditions. All parts scrapped |
To ensure consistent and rigorous execution and reporting, all risks must be evaluated, without deviation, using the standard 5 x 5 risk matrix, likelihood criteria, and consequence criteria to analyze risks.
| Risk Evaluation Scoring Chart | |||||
| L/C | 1 | 2 | 3 | 4 | 5 |
| 1 | Very Low | Very Low | Very Low | Very Low | Minor |
| 2 | Very Low | Very Low | Minor | Minor | Medium |
| 3 | Very Low | Minor | Medium | Medium | High |
| 4 | Very Low | Minor | Medium | High | Very High |
| 5 | Minor | Medium | High | Very High | Very High |
This will correspond to one of five (5) overall levels of risk: Very Low (Dark Green), Low (Green), Medium (Yellow), High (Orange), Very High (Red).
Having identified what events might occur, it is necessary to determine the root causes for these events. There may be many ways an event can happen; however, using the 5 Whys or 8-D processes will allow you to determine the root cause of each event.
Once the root causes have been identified, they will need to be analyzed in terms of their likelihood to occur and the severity of Consequences should they occur. This is accomplished using the Likelihood and Consequence Criteria charts established in section 5 of this process.
Using the scores developed in the risk register, the overall level of risk is determined (Likelihood x Consequence = Level of Risk) using the risk assessment scoring table below, and a risk level between Very Low and Very High is assigned.
- Risk treatment is not required for risks that score in the Very Low (Dark Green) and Low (Green) categories. Monitor and review the risk for future treatment.
- For risks scoring in the Medium (Yellow) category, existing controls must be evaluated for effectiveness. For controls assessed to be less than adequate, evaluate for further risk treatment. (Cost/Benefit – Risk/Reward, etc.).
- All risks scoring in the High (Orange) and Very High (Red) categories will require risk treatment and/or further analysis.
| Score | Impact | Impact Exposure | |
| Management Control Action (MCA) | Timeframe | ||
| 1 to 4 | Very Low | No mitigation and no action is required; the risk is ALARP. Monitor to ensure that the risk remains tolerable at this level. | 1 year + |
| 5 to 8 | Minor | Maintain assurance that the risk remains tolerable at this level. Monitor and manage using routine procedures, unlikely to need specific application of resources (managers and key staff). | Within 9 months |
| 9 to 12 | Medium | Tolerable if the cost of reduction would exceed the improvement gained. Mitigate through management by specific reviews and monitoring procedures (Managers), but regular monitoring should occur. | Within 6 months |
| 13 to 16 | High | Tolerable only if risk reduction is impractical or if the cost is disproportionate to the improvement gained. Mitigate by implementing controls to reduce the risk to as low as is reasonably practicable. Where this cannot happen, continual monitoring should occur. | Within 3 months |
| 17 to 25 | Very High | Intolerable, the risk cannot be justified except in extraordinary circumstances. Mitigate by ceasing all related activities. | Immediate |
Step 4: Respond
For each risk, the risk owner must establish an appropriate level of mitigation. Control measures, in addition to existing controls, may be needed to achieve this level of mitigation. When a response action is completed, the risk should be reassessed (i.e., repeat Step 3) to reflect any newly introduced existing control measure.
Risk treatment is the process of identifying the options for modifying risks and selecting and implementing those options in the form of a risk treatment plan. Once implemented, treatments provide or modify risk controls.
Risk treatment involves the cyclical process of:
- Assessing a risk treatment;
- Deciding whether residual risk levels are tolerable;
- If not tolerable, developing a new risk treatment;
- Assessing the effectiveness of that treatment.
Risk treatment options are not necessarily mutually exclusive or appropriate in all circumstances. The available options can include:
- Avoiding the risk by deciding not to start or continue an activity;
- Accepting or even increasing the risk to pursue an opportunity;
- Removing the source of the risk;
- Changing the likelihood of the risk occurring;
- Changing the consequence of the risk occurring;
- Sharing the risk with another party or parties;
- Retaining the risk by informed decision.
Selecting the most appropriate treatment options involves balancing the implementation costs against the benefits derived. It is essential to consider all direct and indirect costs and all benefits, whether tangible or intangible.
Decisions should account for the need to carefully consider those rare but severe risks that may warrant risk treatment, which are not justifiable on strictly economic grounds. Customer, regulatory, or legal requirements may override simple cost/benefit analysis.
If budgetary constraints exist, the treatment plan should clearly specify the priority order in which treatments should be implemented. If, after treatment, residual risk remains, this risk should be evaluated, and a decision should be made about whether to retain this risk or repeat the risk treatment process.
Step 5: Review
Ongoing review is essential to ensure the management plan remains relevant and effective. The factors that affect the likelihood and consequences of an event may change, as may the factors that affect the suitability or cost of the treatment options.
Regular reviews and challenges are essential to ensure that the residual risks are appropriately managed and that the risk data remains accurate and reliable, reflecting changes in circumstances or management activities.
Our risk and opportunity register template supports this by scoring each risk twice, pre-control and post-control, on a 5×5 Likelihood × Impact matrix, so you can show an auditor what each control actually changed.
Step 6: Report
Regular reports are necessary to inform and assure top management and other key stakeholders that risks are being appropriately managed. Reporting must be based on current process data, which must be updated and reviewed in good time for the reporting cycle.
Occasionally, it may be appropriate to escalate a risk to ensure it is assessed and/or managed by the person or party best placed to do so (able and with appropriate authority). For example, where a more substantial or coordinated response is required than the current owner can authorize or implement, or where the risk severity or its effects in the broader project justify a higher-level assessment and/or management.
Step 7: Monitor
Continuous systematic and formal monitoring of the implementation of the risk process and outputs will take place against appropriate performance indicators to ensure process compliance and effectiveness. Monitoring may take a variety of forms and range from self-assessment and internal audits to detailed reviews by independent external experts.
Other process monitoring, such as quality and delivery performance, as well as actual progress against the treatment plan, should provide information about the effectiveness of the risk management process.

Taking A Planned Approach To Address Risks
Ensure that your organization takes a planned approach to addressing risks and realizing opportunities, and that any actions taken have been recorded.
When deciding how to plan and control the quality management system, including its component processes and activities, your organization needs to consider both the type and level of risk associated with them.
Options to address risks and opportunities can include:
- Avoiding risk
- Taking risks to pursue an opportunity
- Eliminating the risk source
- Changing the likelihood or consequences
- Sharing the risk
- Retaining risk by informed decision
- SWOT analysis by the organization as part of its business strategy to identify the external risks and opportunities, and an action plan to address them
- Formal business risk assessment performed by the organization, taking into consideration its context, associated risk, opportunities, and mitigation plan
The process approach is used by organizations to identify sources of input, activities, output, receiver of output, performance indicators to control and monitor processes, the risks and opportunities associated with them, and an action plan to address them.
How Do I Evaluate Opportunities?
What is an Opportunity?
Opportunities may be identified as positive effects of risks, such as a risk forcing the implementation of a risk reduction measure that is beneficial in a broader context than just reducing a particular risk. An opportunity is also a set of circumstances that makes it possible to do new and positive things, for example:
- Develop new products and services;
- Develop new markets and/or increase market share;
- Improve the work environment;
- Improve productivity;
- Improve operational efficiency (reduction of resource use, reduction of waste, etc.).
Risks may require measures to improve your organization’s working environment. However, these measures also create opportunities to attract better-qualified employees, improve morale and job satisfaction, and reduce staff turnover; the initial risk creates opportunities to improve.
Improvement often does not take place on a ‘continual’ basis. Sometimes, improvement can be affected reactively through corrective actions, incrementally over time, by a step change or breakthrough, creatively through innovation, or by reorganization and transformation.
How to Develop a Business Case
Opportunity evaluation is the process of evaluating an idea, concept, or opportunity to determine whether there is sufficient strategic, market, and financial merit for continued consideration and possible development into a product or category.
If you are looking to develop new products and services, or develop new markets and/or increase market share, develop a business case that includes:
- A strategic analysis of the current sourcing process;
- A completed comprehensive spend analysis;
- A market analysis.
This approach will help you highlight and understand the existing environment and prioritize profit opportunities. Three key areas are suggested to cover all considerations:
- Purchase demand management;
- Supply base management;
- Total cost management.
Identifying opportunities by better understanding and managing interested parties’ needs and expectations can also help reveal business opportunities in all stages of the product lifecycle (from design to end of life).
Conduct a SWOT Analysis
SWOT analysis is a diagnostic tool for strategic planning that involves identifying and evaluating strengths, weaknesses, opportunities, and threats. It is essential to be specific, evaluative, and analytical when compiling and recording the SWOT analysis.
Opportunity evaluation should utilize standard SWOT analysis models. Half an hour is often enough to spend on strengths, for example, before moving on. This will determine the benefits and risks associated with the opportunity and help determine the current strengths and weaknesses within your company’s processes.
List the Opportunities
The approach chosen to determine those opportunities that need to be addressed can include gaining a consensus of opinion from cross-functional representatives on which ones need to be addressed, for example, in a meeting or workshop, or applying criteria in a matrix, for example, using an existing business risk management process.
This step is intended to evaluate the socio-economic, political, environmental, and demographic factors that affect organizational performance. The aim is to identify circumstances in which organizations can exploit and evaluate their possible benefits. Examples include:
- Technological developments;
- New markets;
- Change of government;
- Changes in interest rates;
- Demographic trends;
- Strengths and weaknesses of competitors.
Potential sources of improvement opportunities include the results of analysis and evaluation of process performance, compliance, internal audits, and management reviews. Remember that opportunities may be time-limited, and consider how the organization can make the most of them. Once the opportunities that need to be addressed are identified, your organization should plan actions to act on the opportunities.
Act on the Opportunities
Once the SWOT analysis is complete, you need to address the question of how potential opportunities can be maximized and how the risks implicit in weaknesses and threats can be minimized. Bear in mind that much of the information you have collected will represent symptoms rather than root causes, so further consideration of the underlying issues may be needed.
However good or bad the analysis results are, ensure they are integrated into subsequent planning and strategy development. Revisit the findings at suitable intervals to check that they are still valid.
Taking or not taking an opportunity presents different levels of risk. To evaluate these risks, taking (or not taking) the opportunity is defined as a risk management item, and the associated risks must be evaluated.
The output from the management review should include opportunities for further integration of the management system with other business processes and any implications for the organization's strategic direction.
How Should I Communicate Risks And Opportunities?
Within your quality management system, consideration must be given to internal and external risk communication. Internal communication is necessary for all appropriate personnel to be aware of the remaining risks even after implementing risk control measures.
Your organization should ensure that it has documented and clarified the roles, responsibilities, accountabilities, and authorities at all levels of the business to address risk management. This ensures that a risk management approach is embedded in your operations through a number of communication, training, and support systems, including:
Specific risk management training sessions should be held on an annual basis, aimed at providing an overview of the risk management process. Instruments providing training on appropriate controls include:
- Job descriptions, contracts
- Inductions
- Policies
- Procedures, process maps
- Terms of reference
- Performance planning
To ensure adequate risk management competency levels are achieved and maintained, your organization should provide training in the risk management process and its application.
Risks & Opportunities Procedure - What Might You Document?
- Risk & Opportunity Management Process
- Context
- Identification
- Assessment
- Inherent Risk Rating
- Risk Treatment
- Review
- Reporting
- Monitoring
- Risk Registers
- Risk Appetite
- Training
- Communication

Related Information You Might Find Useful
- Actions To Address Risks And Opportunities [Procedure Template] [ISO 14001]
- Actions To Address Risks And Opportunities [ISO 45001]
 ISO 9001
 Procedures
 Process Maps
 Charts
 Reports & Forms
 Guidance
 eQMS ISO 9001:2026 Risk & Opportunity Management Toolkit
 Reference Guides
 Forms
 Training Presentations


